What Your IP Address, Email, and Browser Together Tell a Website
See what your IP address, email, and browser fingerprint each expose alone, and how cross-referencing all three in server logs creates a far stronger record.
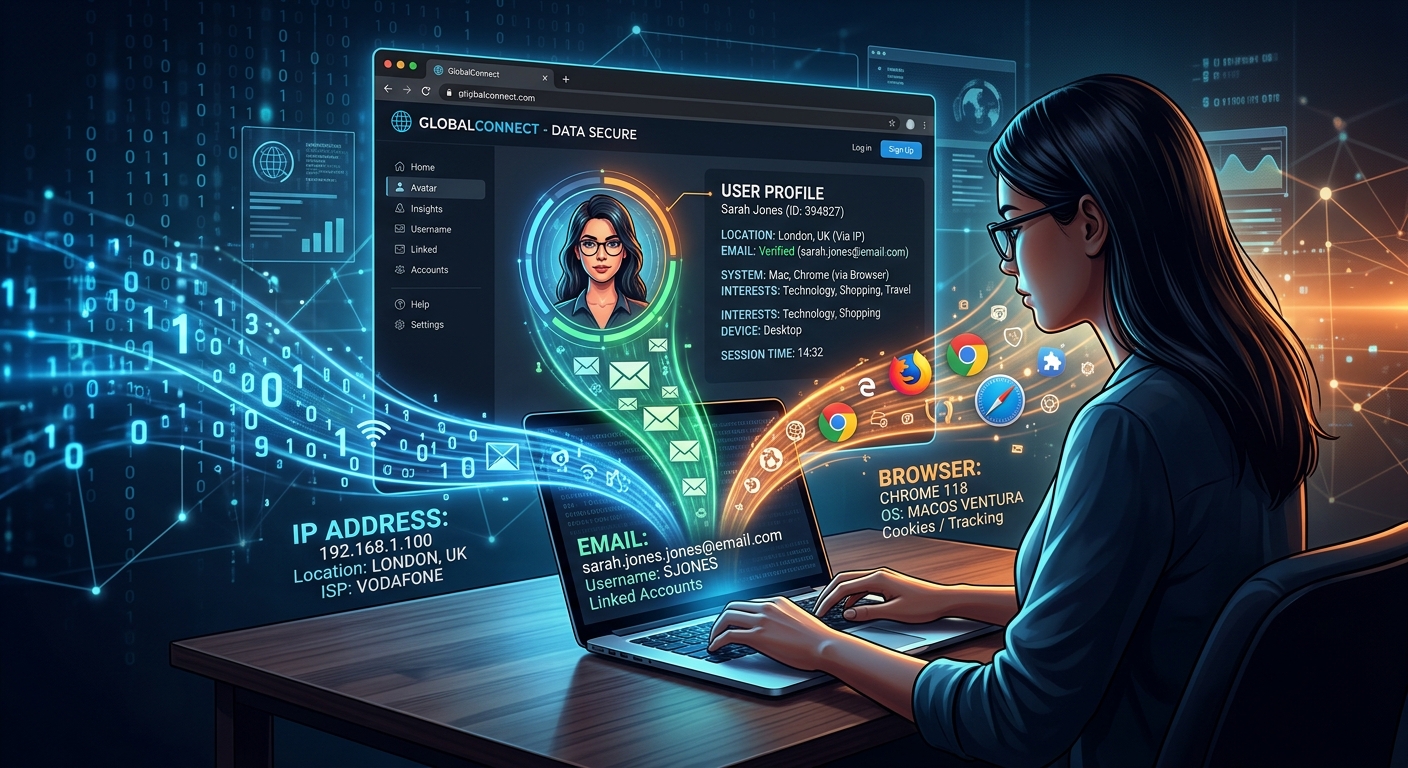
Three pieces of data, sitting in the same server log, rarely get discussed together. Most privacy conversations pick one: your IP address, or your email address, or browser cookies. But the real picture emerges when you look at all three at once, because each one patches the gaps the others leave behind.
What These Three Signals Tell Websites
- Your IP address reveals your approximate city, your ISP, and your network block, but not your name or street address.
- Your email address is a permanent, globally unique identifier that links your account across every future session.
- Browser fingerprinting collects passive attributes from your browser and device without cookies, and it often persists across network changes.
- Cross-referencing all three in server logs creates a far more durable identity record than any single signal alone.
- Practical steps at the account creation stage can break the linkage between your real identity and that combined record.
What an IP Address Can and Cannot Tell a Server
Your IP address is the first thing a web server records when your browser makes a request. It has to. Without it, the server cannot route data back to you.
What the server can read from that IP depends on the address and the databases mapped to it. In most cases, a residential IP will point to a city or metro area, an internet service provider, and an autonomous system number. That is the block of addresses your ISP or organization owns. The mapping is reasonably accurate at the city level for home connections. For corporate networks, it can be quite precise, because the ASN maps directly to a named organization.
What an IP address does not tell a server is your name, your street address, or your personal identity. That requires a legal request to your ISP, not a database lookup. The distinction matters and it is worth holding onto as you read further.
Dynamic IP addresses complicate the picture further. Many residential connections rotate on a schedule set by the ISP, sometimes daily. A website logging your IP today may see a completely different address from the same household next week. Over longer periods, IP alone is a leaky identifier.
The Weight an Email Address Carries
When you create an account on a website, you hand over something considerably more persistent than an IP address. An email address does not rotate. It does not change when you switch networks. It survives VPNs and proxies and remains tied to you indefinitely.
An email address is also globally unique by design. Two users cannot hold the same address simultaneously. This makes it an excellent primary key in a database, which is exactly how most account systems treat it.
The moment your email is stored alongside a timestamp and an IP address, two previously separate signals are joined. The server now knows that whoever held IP address X at time T chose to register with email address Y. If that email connects to a real name through a prior login or a payment record, the chain extends further still.
This is not speculation about what websites might do with that data. It is a description of what server logs contain by default. Whether any given operator ever queries that data in a meaningful way is a different question, with a more reassuring answer in most cases.
Browser Fingerprinting: The Signal You Did Not Consent to Share
The third signal is the quietest of the three. Browser fingerprinting collects attributes from your browser and device without setting a single cookie. No storage permission is required. No opt-in banner applies to it.
The attributes themselves are individually mundane. Your screen resolution. Your browser version. Your operating system. Your installed fonts. Your time zone. Your canvas rendering signature. Each one is common. But the combination of fifteen or twenty of them starts to narrow the field considerably. The W3C's published guidance on browser fingerprinting surface area documents exactly how many attributes contribute to this signal and why reducing it at the specification level is architecturally difficult.
Unlike an IP address, a browser fingerprint tends to persist across network changes. Connect from a coffee shop instead of your home network and your IP changes. Your browser fingerprint stays the same. This makes fingerprinting complementary to IP logging rather than redundant with it.
What Goes Into a Browser Fingerprint
A typical fingerprinting script collects the following data points, roughly in order of identifying power:
- User-agent string , your browser name, version, and operating system, all delivered in one line with every request.
- Screen dimensions and color depth , your display's pixel resolution and bit depth, which vary by hardware.
- Timezone and language settings , your locale configuration, independent of where your IP address geographically resolves.
- Canvas fingerprint , a hash generated by rendering a hidden image, which varies by GPU model and font rendering engine.
- WebGL renderer , reveals your graphics hardware in considerable detail, often including the specific GPU model name.
- Installed plugins and MIME types , less informative in modern browsers, but still collected by many scripts running today.
- Audio context fingerprint , derived from how your browser's audio processing stack handles a test signal, which differs by hardware and driver version.
None of these require you to accept cookies. None require elevated JavaScript permissions beyond what any standard page already uses. They are passive reads on your environment, available to any script that runs during your visit.
Cross-Referencing Changes What Any One Signal Could Do Alone
The most important point in this article is not about any single signal. It is about what happens when all three land in the same log entry.
A server that records your IP, your fingerprint attributes, and the email you registered with has effectively created a three-way join. Even if you log in from a new IP six months later, the fingerprint may match the original session. Even if you create a second account with a different email, the same IP-plus-fingerprint combination may appear in both records. Even if your IP rotates, the email and fingerprint bridge the gap.
This is not a dramatic claim. It is relational database logic applied to routine web server data. Each signal covers the other's weaknesses. IP addresses are unstable, so the email and fingerprint anchor the record. Emails can be changed, so the IP and fingerprint provide continuity. Fingerprints shift with major browser updates, so the email and IP hold the history together in the meantime.
How Each Signal Holds Up As an Identifier
| Signal | Persistence | Collection Method | Main Weakness | Survives a VPN? |
|---|---|---|---|---|
| IP Address | Low to medium | Automatic on every request | Rotates on dynamic connections | No, replaced by VPN exit IP |
| Email Address | Very high | Only at account creation or login | Requires user action to collect | Yes, unchanged by network |
| Browser Fingerprint | Medium to high | Passive JavaScript during page load | Changes with browser updates or new hardware | Yes, unaffected by VPN tunnel |
The Account Creation Moment Is the Binding Event
Of the three signals, two of them, IP and fingerprint, are collected passively on every page load regardless of what you do. The email address only enters the picture when you create an account or log into one.
That registration event is where the passive record gains a name. Before it, the server has an anonymous visitor with a fingerprint and an IP address. After it, that visitor has an email address attached to every future session that shares those two signals.
For most everyday browsing this has limited practical consequence. But consider what happens when an IT administrator or a developer needs to evaluate a new SaaS platform or test how a service behaves for a first-time user. A test signup using a real work email on a new service means that address is now permanently associated with the IP block of the organization's network, plus whatever browser fingerprint the test machine presents. That record sits in the vendor's database for as long as they retain logs.
Using a random email generator for that kind of low-stakes evaluation is a practical way to avoid that linkage. The IP address is still logged, because it has to be. But the email that would anchor a durable identity record is disposable. No network reconfiguration is required. No VPN policy change is needed. The binding event simply never creates a lasting tie back to a real identity.
What These Signals Actually Reveal Versus What They Can Theoretically Expose
It is worth being direct about the gap between technical capability and real-world practice.
For most websites, including content sites, small developer tools, and independent SaaS products, the server logs holding this data are never queried for individual user profiling. They exist for debugging, rate limiting, and abuse prevention. The three-way join described above is available to anyone with database access, but it is rarely assembled in practice.
The scenarios where it genuinely matters are narrower: account fraud investigations, ad-tech platforms with cross-site tracking infrastructure, services that build behavioral profiles for commercial targeting, and compliance audits. Knowing which category a given service falls into requires reading their privacy policy and, often, a realistic assessment of their business model and underlying incentives.
The honest position is that most websites are not actively building identity graphs from your IP, your email, and your fingerprint. But the data that would allow them to do so is collected by default and persists for as long as those logs are retained. That is a factual observation, not a warning.
Three Signals, One Persistent Record: What the Full Picture Actually Shows
Your IP address is a routing identifier with a loose geographic attachment. Your email is a persistent, globally unique identity handle. Your browser fingerprint is a passive, cookieless signal that follows your hardware and software configuration across every network you connect from.
Together, they produce a record that is more durable and more linkable than any single signal suggests on its own. The account creation event is the moment that binds the passive signals to a real identity, which makes it the step most worth thinking about when the service is new, the stakes of identification are low, and the email address involved is a real one tied to a person or an organization.
Understanding these signals does not require alarm. It requires accuracy. The data exists, the cross-referencing is technically straightforward, and the practical risk depends heavily on who holds the logs and what they have reason to do with them. That is a fact worth knowing, and a question worth asking about any service you evaluate or sign up for.